Official Recognition | SoftSafe Technology’s Open-Source Software Composition Analysis Tool System V2.6 Awarded SBOM Tool Capability Evaluation Certificate
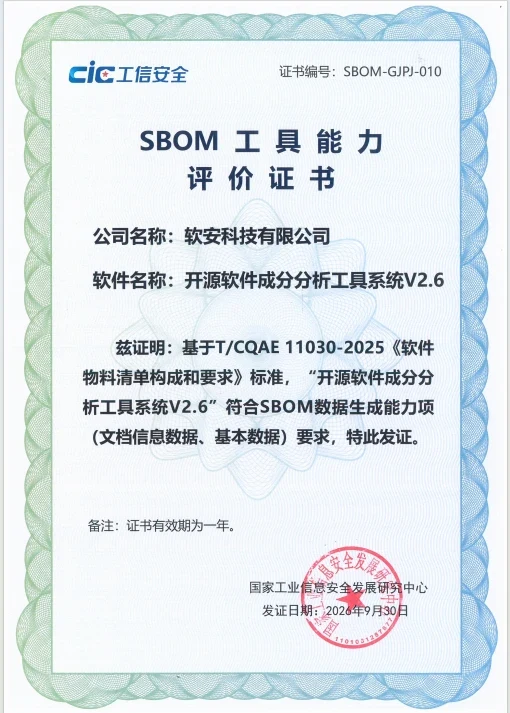
Introduction: Strengthening the foundation of software supply chain security, with product capabilities officially recognised by a national industrial information security authority.
Recently, SoftSafe Technology Co., Ltd.’s Open-Source Software Composition Analysis Tool System V2.6 successfully passed an assessment conducted by the China Industrial Control Systems Cyber Emergency Response Team (CICS-CERT), under the National Industrial Information Security Development Research Center, and was awarded the SBOM Tool Capability Evaluation Certificate (Certificate No.: SBOM-GJPJ-010). This achievement confirms that the product’s core SBOM data generation capabilities meet industry standard requirements.
As digital industries continue to expand and open-source technologies are adopted on an increasingly large scale, software supply chain security risks are becoming more prominent. A Software Bill of Materials (SBOM) is a key tool for identifying software assets, managing open-source vulnerabilities and mitigating licence compliance risks. It has become a fundamental capability for effective software security governance.
The assessment was conducted in strict accordance with T/CQAE 11030-2025, Software Bill of Materials: Composition and Requirements. It provided a comprehensive and rigorous evaluation of the tool’s SBOM generation capabilities across two core dimensions: document information data and basic data.
The standard specifies detailed functional and performance requirements for SBOM tools, covering format support, generation depth, capability types, usability and compatibility, among other aspects. Open-Source Software Composition Analysis Tool System V2.6 successfully met all capability requirements specified by the standard and was awarded the official certificate.
As an authoritative organisation directly affiliated with China’s Ministry of Industry and Information Technology (MIIT), the National Industrial Information Security Development Research Center is recognised for its work in industrial information security, software supply chain security standards development and technical tool assessment. This certification provides official recognition of SoftSafe Technology’s technical capabilities and its ability to implement relevant standards in practice.
Open-Source Software Composition Analysis Tool System V2.6 focuses on software composition analysis and SBOM generation. It accurately identifies open-source components within software and generates standardised, compliant SBOMs. By helping organisations establish a clear inventory of their software assets and improve component-level transparency, the tool provides a reliable data foundation for vulnerability identification, open-source licence compliance audits and software supply chain risk management. It is suitable for software security initiatives across a wide range of sectors, including government and enterprise, financial services, industry and IT innovation.
Obtaining this certification is not only an achievement but also a commitment to greater responsibility. Looking ahead, SoftSafe Technology will continue to strengthen its expertise in software supply chain security, keep pace with evolving SBOM standards and further enhance its product capabilities. The company will continue to optimise the entire process, from SBOM generation and software composition analysis to risk assessment, helping more organisations build secure and trusted software supply chains and contributing to the secure, high-quality development of the digital economy.