
SoftSafe Tech joins the SBOM working group of the Open-Source Risk Governance Lab
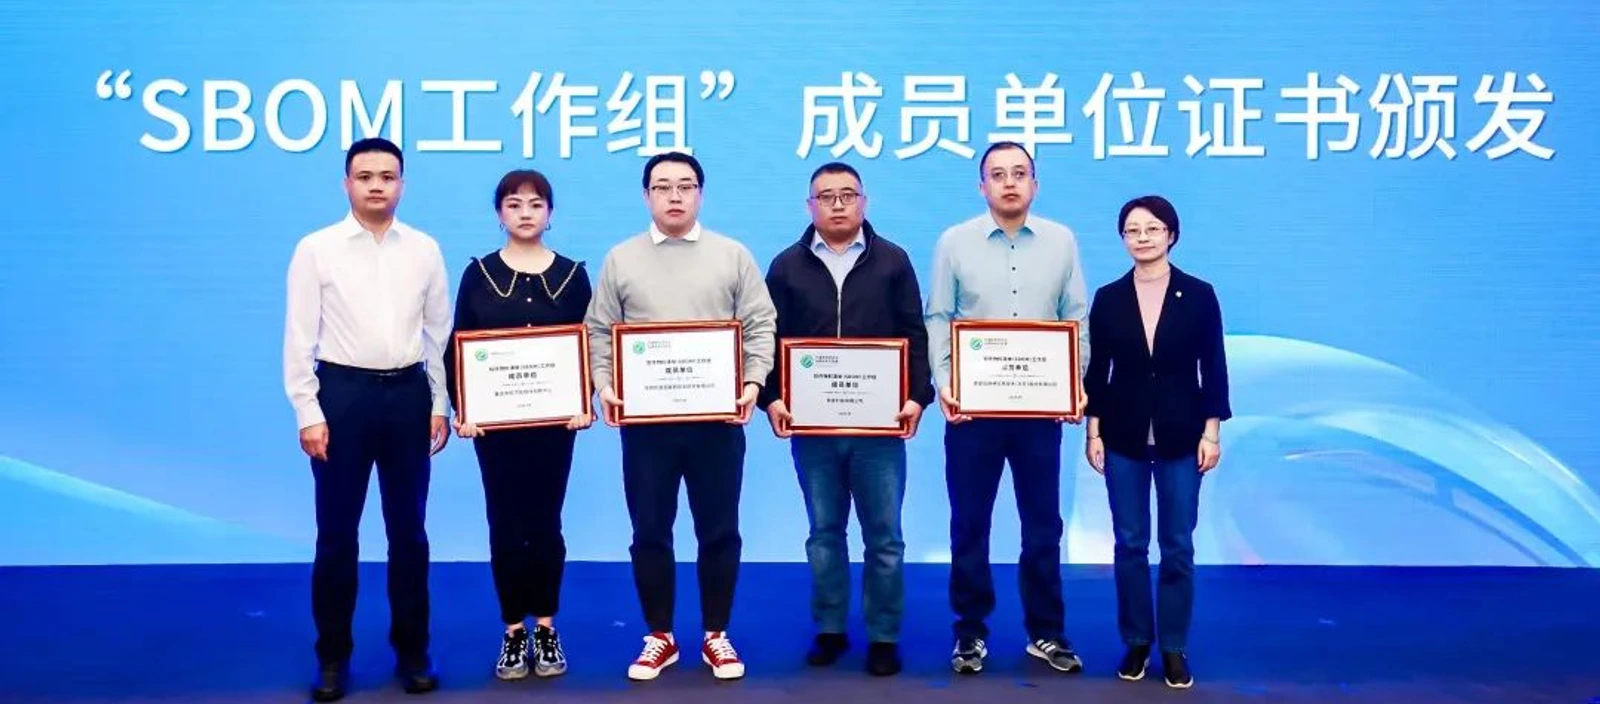
SoftSafe Tech became a founding member of the SBOM working group at the 2024 Open Source Ecology Conference, participating in areas such as software material information management, standard formulation, and technical exchanges. The goal is to promote transparency and traceability of supply chain software components.
The conference took place from September 25 to 27, 2024 in Beijing. At the Software Material List (SBOM) forum announcement, the National Information Industry Security Development Research Center awarded certificates to the founding members of the working group.
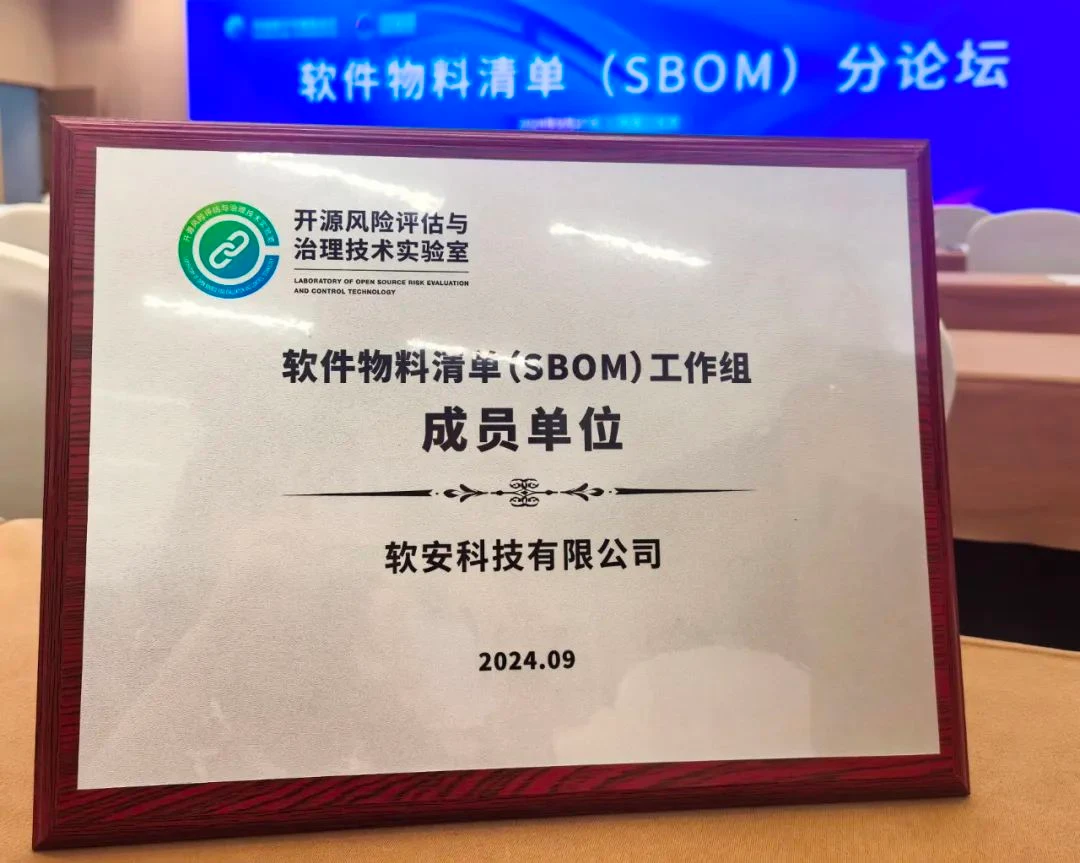
Areas covered by the working group
SBOM is used to document components, versions, sources, and dependencies within software. The working group will engage in discussions on information formats, risk assessments, and industry applications, aiming to facilitate the transmission of SBOMs between suppliers, development teams, and users.
From inventory integration to risk remediation
SoftSafe Tech will leverage its experience in identifying components within source code, binaries, and containers to participate in relevant work. When enterprises use SBOMs, they also need to associate component records with vulnerability assessments, license obligations, supplier materials, and specific release versions.
Subsequent participation will be based on the open arrangements of working groups and specific projects, focusing on validating how standards requirements are implemented in reproducible software supply chain governance processes.