
OpenAnolis community visits SoftSafe Tech to discuss software supply chain security and SBOMs
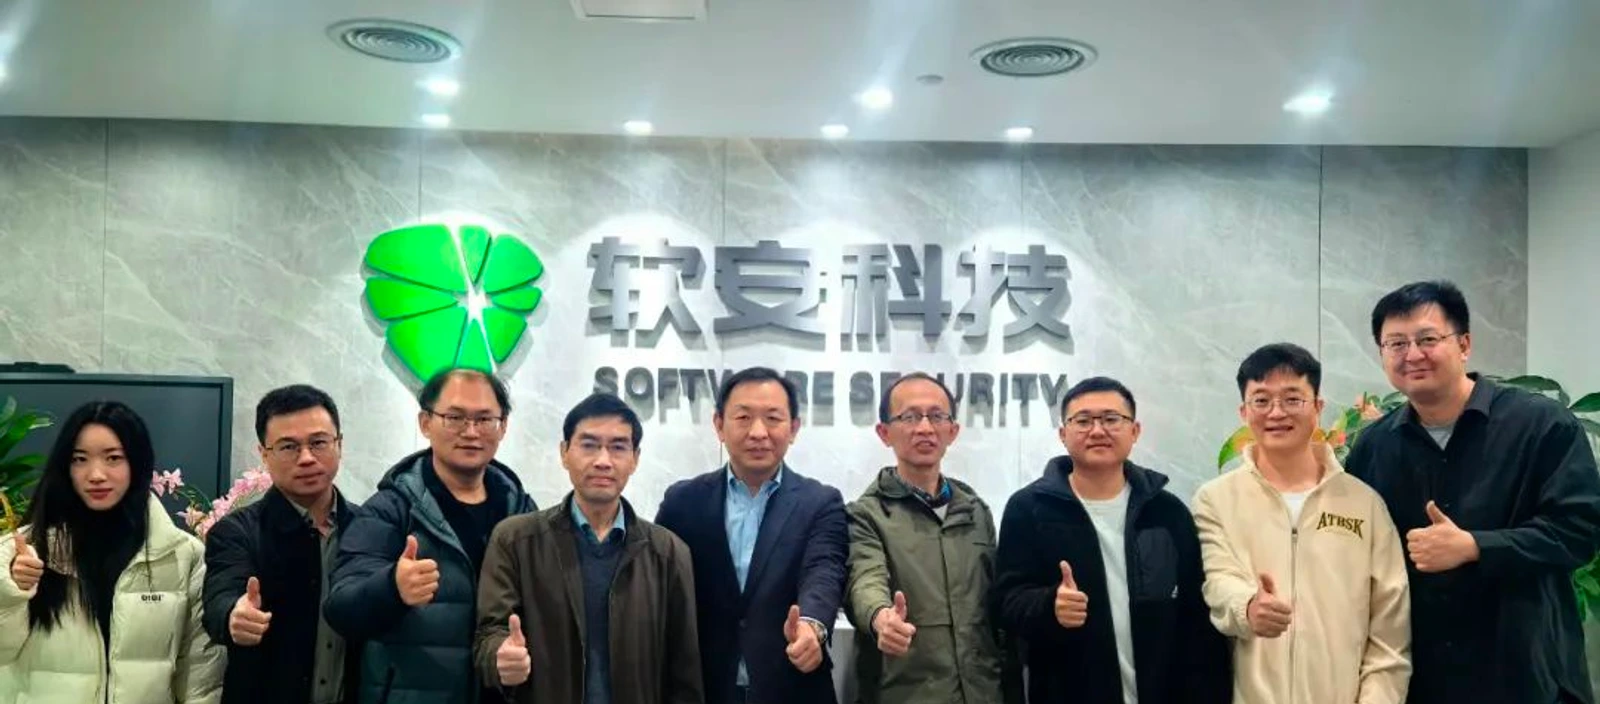
The LongArch Community held a series of visits at SoftSafe Tech's Chengdu site. Enterprise technical representatives discussed software supply chain security, code safety, and fuzz testing. The discussion also covered SCA component identification, vulnerability analysis, and the alignment of SBOM services with operating system scenarios.
The visit invited security professionals from enterprises such as Inspur Information, Alibaba Cloud, and ZTE Communications to participate. SoftSafe Tech introduced its products and related work in the LongArch Community's safety ecosystem.
Topics discussed
Attendees exchanged practical experience on open-source component identification, vulnerability impact assessment, static code analysis, and protocol fuzz testing. The focus of the discussion included how to enhance component information coverage, how to map SBOMs to specific operating system versions, and how to integrate detection results into issue resolution processes.
Adapting to OpenAnolis scenarios
As a member of the LongArch Community's security alliance, SoftSafe Tech will continue to participate in collaborative efforts related to software supply chain security. The goal is to align SCA and SBOM services with the commercial version of the LongArch operating system scenarios and validate data and processes based on actual projects.
The OpenAnolis community is a server operating system–oriented open-source community. Subsequent exchanges will be based on public projects, community rules, and specific collaboration content.